

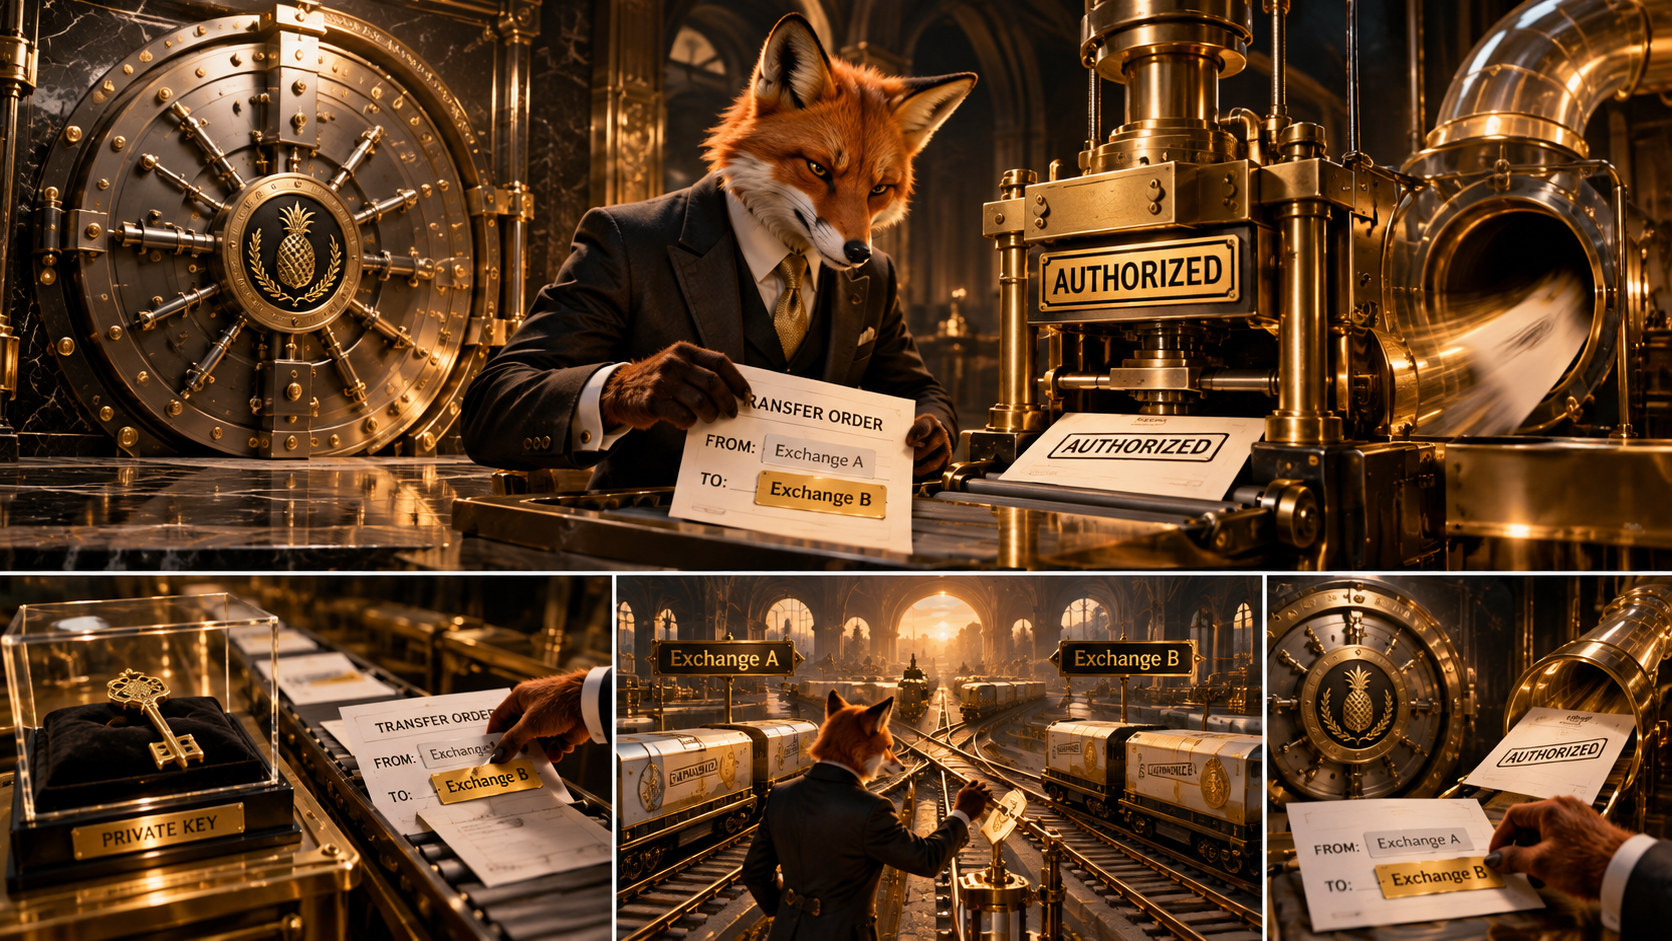
Bitget says its private keys were not compromised. The harder question is what a valid signature proves when the instruction being signed cannot be trusted.
Bitget says attackers compromised a critical backend wallet component, manipulated transaction information, and caused the exchange's own authorization process to approve unauthorized transfers. The company later placed the loss at approximately $387.5 million after expanding its accounting to include additional transactions.
What is confirmed
- Bitget says it detected unauthorized transfers at 18:31 UTC on September 24, 2026.
- The company initially reported approximately $351.6 million in affected assets and later revised the figure to about $387.5 million as additional Zcash and TRON transactions were included.
- Bitget says private keys were not compromised and cold wallets were unaffected.
- Withdrawals were suspended while the exchange investigated and contained the incident.
- Bitget says the vulnerability has been identified and remediated, with Mandiant and SlowMist assisting.
What remains unknown
The public record does not yet establish the initial-access path, the exact backend component compromised, how attacker-controlled transaction data reached the authorization layer, or why independent on-chain analysis observed outflows continuing after Bitget's stated detection time. North Korean involvement has been suggested by outside analysts but has not been definitively established.
Why it matters
If Bitget's account survives independent investigation, the incident separates two controls that are often treated as one. Cryptographic signing can prove that an approved signing process produced a valid signature. It does not automatically prove that the business instruction presented to that process was legitimate. Transaction intent, destination integrity, authorization context, and signing authority need independent controls before an irreversible transfer is approved.
What TensileVue is watching
The next important evidence is the detailed root-cause analysis: which component was compromised, what validation existed between transaction construction and signing, how containment occurred, and why transfers may have continued after detection. Until that evidence is public, mechanism findings should remain bounded to Bitget's own account and independently observable chain activity.
Sources
- Bitget initial security notice, September 24, 2026
- Bitget incident update, September 25, 2026
- The Block incident reporting
- TRM Labs analysis
- Bitquery on-chain investigation
Developing story: This article reflects the public record available September 26, 2026 and should be updated if Bitget, Mandiant, SlowMist, law enforcement, or independent blockchain analysis materially changes the record.